Compliance calendar maps EU requirements for AI Act, NIS2 and DORA
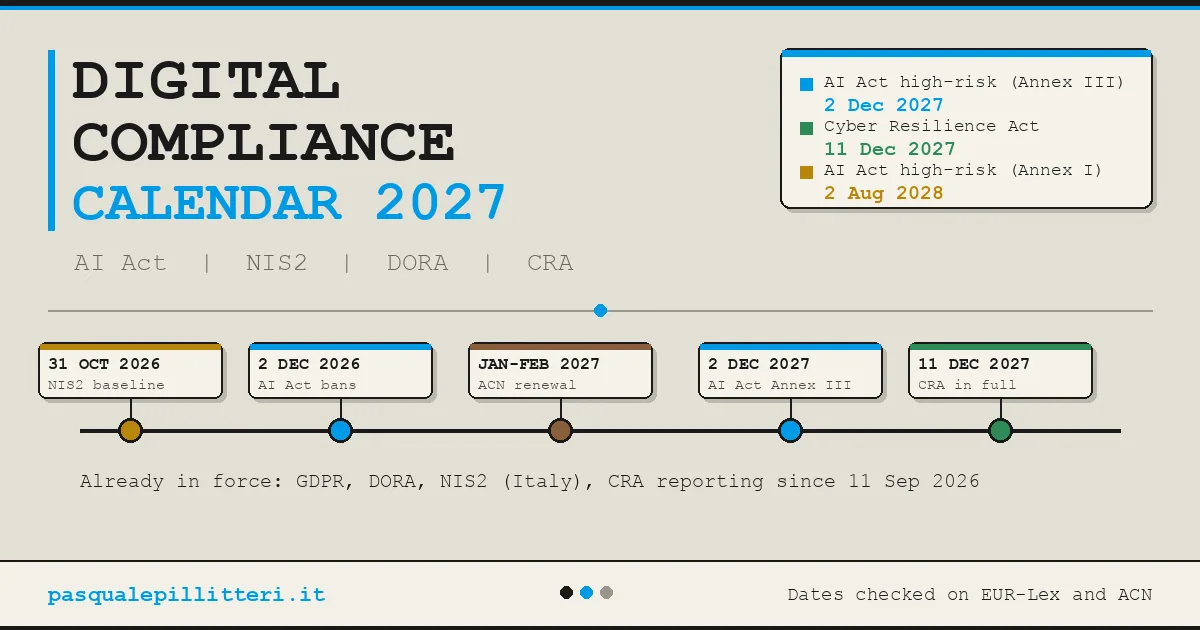
A compliance calendar outlines the deadlines for EU digital regulations including the AI Act, NIS2, DORA and the CRA, with a key date of 2 December 2027. The compilation structures requirements for technology and security officers.
What happened?
A new compilation maps the timelines for the EU's parallel regulations in technology and cybersecurity: the AI Act, NIS2, DORA and the Cyber Resilience Act (CRA). The calendar details corporate obligations and specific deliverables leading up to a noted deadline of 2 December 2027. The review structures requirements based on roles, certification demands and sanction levels.
Key facts
| Publiceringsdatum för kalendern | 11 januari 2026 |
|---|---|
| Specifik tidsfrist i tidslinjen | 2 december 2027 |
| Omfattade regelverk | AI Act, NIS2, DORA, CRA |
Why it matters
Several significant EU legislative acts are coming into force in overlapping phases, creating a risk of duplication and regulatory friction for European organisations. Coordinating compliance for AI and cybersecurity reduces the risk of sanctions and facilitates technical adjustments. The calendar clarifies which sub-requirements must be met at specific intervals.
Who is affected?
The requirements affect companies that develop or implement AI systems, providers of connected digital products, as well as financial actors and critical infrastructure providers. Executive boards, IT security managers and legal counsel are all impacted in the planning of regulatory compliance.
Impact on the EU
The regulations are binding across all EU member states. Together, the AI Act, NIS2, DORA and the Cyber Resilience Act set requirements spanning the union's entire digital infrastructure, from software developers to financial institutions.
What else you should know
The compliance calendar also highlights the interaction with established standards such as ISO 27001 for information security and ISO 42001 for AI management systems. It also illustrates how sanctions differ between the directives.
Quick answers about this story
Vad har hänt?
När hände det?
Varför spelar det roll?
Vilka bolag berörs?
The link opens in a new window and leads to the publisher's own site.
Källan har spårats automatiskt från utgivaren via Aheadlines signalkedja.
AI-verktyg i artikeln
Topics
Get similar news straight to your inbox
The reader's room
Send in a question or an addition. The newsroom reads everything before it's published and replies when relevant. No AI-generated text – just people.
Sign in to submit a comment or question.
Read the article through your role
- Decide whether this affects strategy over 6–12 months or is just noise.
- Discuss with leadership: do we own the right question or does ownership need to move?
- Ask: what risk are we taking by NOT acting on this this quarter?
Generated angle — not editorial analysis of "Compliance calendar maps EU requirements for AI Act, NIS2 an"